AI & Automation · Readiness · 15 min
AI Integration Readiness: What Your Data, APIs, Permissions and Governance Need Before Production AI
The model is one layer; examine data, tool access, identity, oversight and failure behavior before production AI.
By Umar Uddin · Cloud & Emerging Technologies Engineer
Published 27 September 2026
Meet the Xyncwave team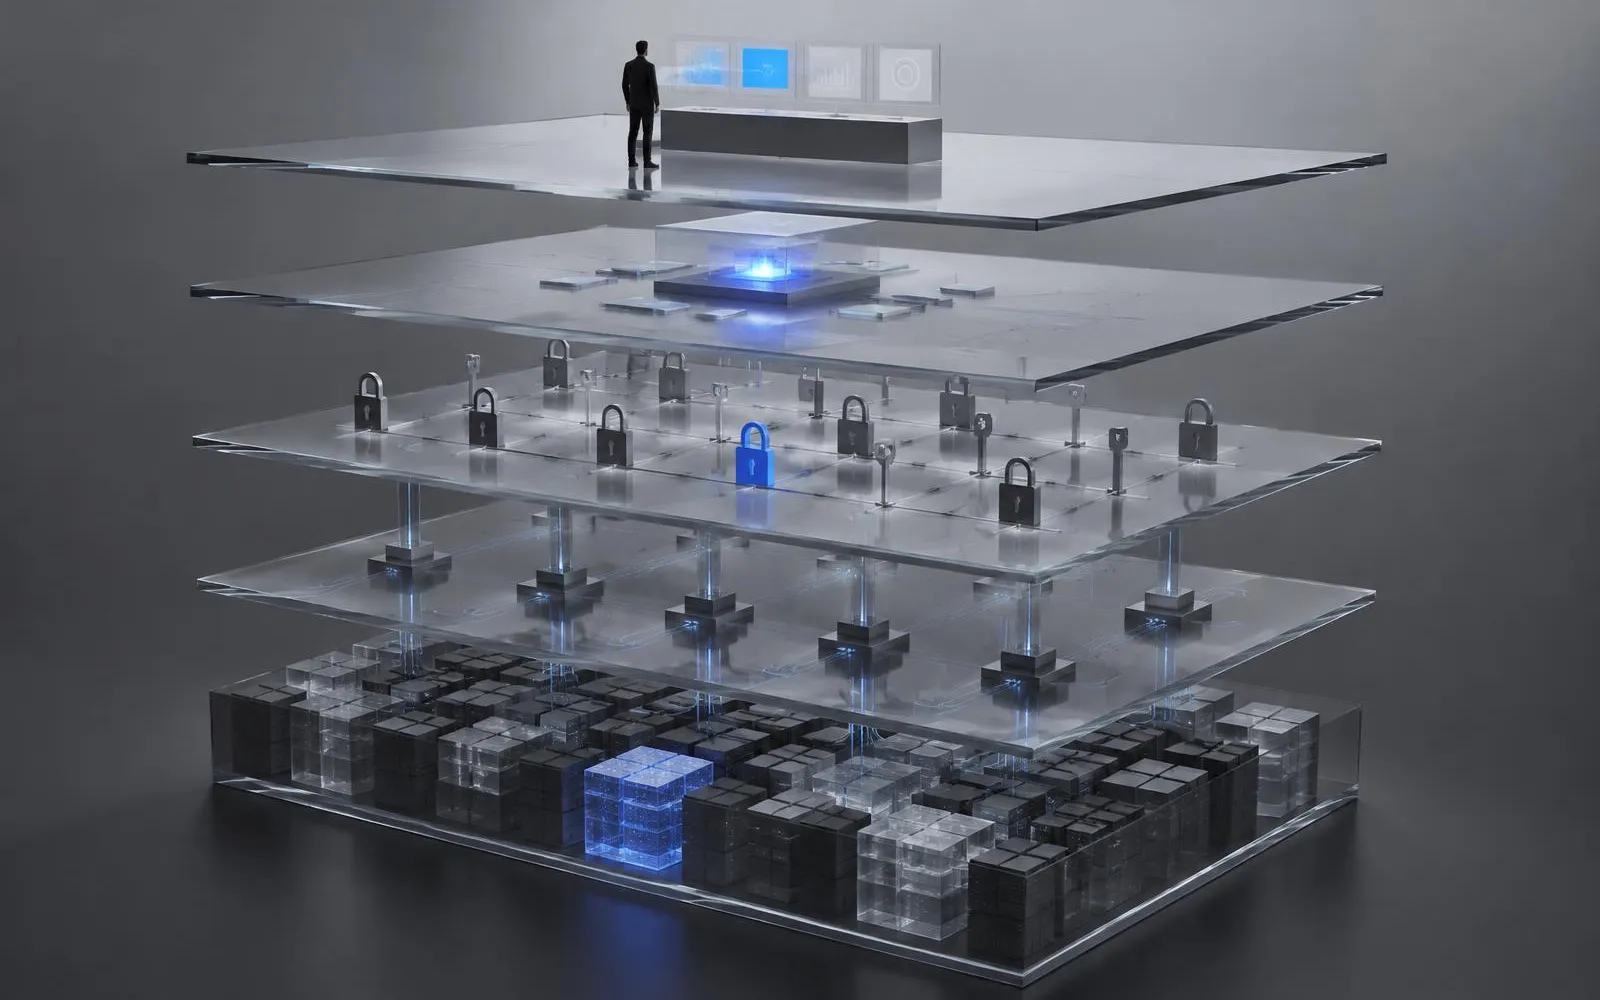
Direct answer
Are our systems ready to support production AI?
A promising AI use case is not the same as an operable AI workflow. Check whether relevant data and knowledge are available and current, APIs and tools expose controlled actions, identities enforce permissions, sensitive information is protected, human escalation is defined and output, cost and errors can be monitored before connecting a model to business operations.
Key takeaways
- Decide what business action AI would support before selecting a model.
- Trace source knowledge and permissions through to the eventual user.
- An AI tool call needs authorization, audit and a safe failure path.
- Pilot with representative exceptions and human review before production deployment.
- Sometimes repairing the workflow or data foundation is the better first investment.
The AI Integration Readiness Stack
Business Workflow → Data & Knowledge → APIs & Tools → Identity & Permissions → Governance & Human Oversight → Monitoring & Measurement.
Start with the job to be done and the person accountable for it. Can the team describe the inputs, decision boundary, correct output and unacceptable error? Identify source records and knowledge, then the tools the workflow must use. Check whether these tools support scoped access and how identity flows through each action. Set oversight and measurable operational signals around the whole chain.
The model is only one layer. A stronger model cannot grant authorized access to missing knowledge, repair contradictory records or explain who should approve a consequential action. This stack is a readiness lens, not a maturity rating or claim about a deployed Xyncwave agent.
Begin with a real decision or workflow, not a model demonstration. Name its owner, inputs, permitted actions, exception routes and acceptance criteria. A team cannot evaluate an AI-assisted process if it cannot explain what a correct human decision looks like or who handles a disputed output. Map the existing workflow before introducing automation: which steps require judgment, which are deterministic and which contain sensitive information? The result is a scope that can be governed and tested rather than an open-ended aspiration to 'add AI'.
Readiness is layered. A plausible use case needs authoritative knowledge, a way to retrieve only permitted context, suitable tool interfaces, identity controls, human review where necessary and monitoring after launch. A strong model cannot repair a missing owner for an outdated policy or an API that grants broad administrative rights for a narrow task. Treat each layer as a question with a named answer. If one layer is absent, a limited advisory pilot may be sensible while action-taking automation is not.
Define the unhappy path as carefully as the demonstration path. What happens when the answer is uncertain, the requested document is missing, a tool times out or a human reviewer disagrees? The workflow should state whether the system stops, asks for clarification or routes to a person. The ability to recover safely and explain the decision is part of readiness, not a post-launch enhancement.
A readiness workshop can rank use cases by consequence and controllability. A read-only internal summary based on governed documents is a different starting point from automated changes to financial or medical records. For each candidate, ask whether an incorrect output can be noticed before it causes harm, whether a human can correct it and whether the underlying information can be verified. This helps teams choose a sensible first pilot without pretending that every use case shares the same safety threshold.
- 01Business Workflow
- 02Data & Knowledge
- 03APIs & Tools
- 04Identity & Permissions
- 05Governance & Human Oversight
- 06Monitoring & Measurement
Verify the data and knowledge path
Useful output depends on trustworthy inputs and an explicit boundary for what may be retrieved.
Inventory the documents and records needed for the proposed task. Note owners, freshness, access restrictions, conflicting versions and the path for corrections. A demonstration against a carefully curated document may fail against live operations with revoked permissions or outdated policies. Test the actual retrieval path, including a question the system cannot answer safely.
When a process has no agreed source of truth, improving that process may create more value than layering an assistant onto it. Link every proposed AI feature to a known information owner and a decision that can be checked.
A retrieval system needs more than a collection of documents. Record who owns each source, when it was last approved, what audience may see it and when it expires. A current policy and an obsolete procedure may contain similar phrases; without version and authority metadata, the wrong one can appear equally credible. Test ambiguous queries, contradictory records and customer-specific exceptions. When the answer cannot be grounded in permitted current material, the system should say so rather than fabricate a confident instruction.
Apply access rules before content reaches the model. A user's permission to see one account should not become permission to search all customer records through a conversational interface. Scope retrieval by the user's identity and purpose, minimize sensitive fields and document retention for both prompts and outputs. Fine-tuning is not a substitute for access control. Include a procedure for removing a superseded document and checking that future responses no longer rely on it.
Quality is partly an ownership question. If two departments maintain conflicting instructions, an AI system will expose that disagreement rather than solve it. Resolve the authoritative source and escalation path for each knowledge domain before increasing automation. Where decisions depend on changing business rules, involve the domain owner in reviewing test cases and subsequent updates.
Treat tool access as a production integration
A model's ability to propose an action does not authorize it to execute that action.
Define user identity, service identity and permission checks separately. Limit available tools to the work required, validate inputs and keep a record of who requested, approved and performed an action. Plan for prompt injection, sensitive-data exposure and unintended tool use. Escalate high-impact or ambiguous decisions to an accountable person.
An API that works for an internal engineer may be unsuitable as an AI tool without narrower scopes, rate limits, reversible operations and an audit trail. Review failure behavior: if a provider times out or returns an uncertain answer, does the workflow stop, retry safely or ask a person?
Separate read-only assistance from action-taking. Reading a permitted knowledge source carries a different risk from changing a record, sending a notification or initiating a refund. Define tool-level permissions for each action, validate arguments server-side and require approval for consequential steps. Limit rate and cost of tool calls so a loop cannot repeatedly act or consume unbounded resources. Prefer operations that can be previewed, confirmed and reversed where the underlying business process permits reversal; where reversal is impossible, increase review before execution.
The action record should connect the user's request, retrieved context, proposed operation, authorization, tool response and final state. Protect sensitive content in those records and make access to them intentional. A human approval is meaningful only if the reviewer can see what will be done and on what basis. Do not treat a model's text as proof that a downstream system actually changed; verify the tool result and reconcile the resulting state.
Prompt injection and misleading retrieved content are operational threats, not merely unusual prompts. An instruction inside an external document should not override tool permissions or the user's authorized task. Test attempts to request another account's data, bypass an approval step or repeat an action. The defense is layered: constrained tools, scoped identities, validation, review and monitoring. No single prompt can guarantee safe behavior.
Review tool interfaces from the perspective of least privilege. An API that exposes a broad update operation may be convenient for a human administrator but unsuitable for an assistant carrying out one narrow task. Create constrained operations with validated parameters and task-specific access rather than relying on a natural-language instruction not to misuse a powerful endpoint. Consider rate limits and execution budgets, and define whether a failed call can be retried without a duplicate effect. If an action cannot be reversed, make that limitation visible at the review point.
An audit trail should explain what happened without becoming an unrestricted copy of sensitive prompts and records. Set retention, redaction and access appropriate to the information involved. Link the human approval to the exact action approved; a broad approval of a conversation is not necessarily approval of every later tool call. Test whether an operator can distinguish a model suggestion, a human confirmation and a verified change in the target system.
Interactive planning tool
AI Integration Readiness Assessment
Review the production foundations for one concrete AI-assisted task.
Is the task and acceptable error clear?
Pilot a bounded workflow before production
Measure the operational task and its exceptions, not just a polished answer in a demonstration.
Select a use case with an accountable owner, representative inputs, a known evaluation method and a human fallback. Test erroneous responses, unavailable tools, contradictory information and unusual permissions. Record what a reviewer changed and why, then define which failures block rollout.
Plan monitoring for quality, latency, usage, cost, access and escalation. A proof of concept may reveal the need for better APIs, source governance or process redesign. Published Xyncwave case studies demonstrate integration and data engineering capabilities; they do not establish a production agentic-AI outcome.
A useful pilot has a bounded task, representative examples and failure cases collected with the people who perform the work. Measure whether outputs are grounded, whether reviewers accept or correct them, how long review takes and what kinds of errors remain. Set stopping conditions for unacceptable responses or unauthorized actions. Keep evaluation data separate from live production information where feasible, and make clear which aspects of the pilot have not been tested in a production environment.
Include the hidden labor in the result. If subject-matter experts spend more time checking and correcting a draft than they spent producing the original, the use case may need better source material, narrower scope or no automation. Review rejected outputs for patterns before changing models. A pilot should end with a decision: expand with controls, revise the workflow or stop. That decision is more valuable than a compelling demo with no path to ownership, monitoring and support.
For a controlled example, imagine an assistant that drafts a response to a customer's operational question. It should retrieve only documents the assigned agent can view, cite the relevant current policy and mark uncertainty when the question falls outside it. A human reviewer approves the draft. The pilot can record where the model chose the wrong source, where the source itself was ambiguous and where the reviewer needed to rewrite the answer. Those are different problems and lead to different interventions: retrieval rules, knowledge ownership or workflow redesign.
Do not expand the same assistant into action-taking merely because drafting performs well. Updating a customer record needs scoped identity, validated fields, an approval policy and a way to detect if a tool call succeeded after a timeout. A refund or notification may have consequences that cannot be casually undone. Introduce actions one at a time, with a dry-run representation where practical and an explicit human checkpoint when risk warrants it. Monitor rejected requests and unexpected tool usage as well as completed work.
Agree who owns the model configuration, knowledge index, API permissions, review policy and incident response. Those owners may sit in different functions. If a pilot cannot identify them, its most useful finding may be an organizational readiness gap rather than a model shortcoming.
Invite the workflow owner and a person who handles exceptions to review the pilot cases together. Their disagreements may expose undocumented policy or contradictory source material before a model is involved. Record which questions remain unresolved, who may settle them and how updates reach the deployed workflow. That preparation makes evaluation repeatable as the system and business rules change.
Buyer questions
Frequently asked questions
Evidence register
Research & Sources
- 01NIST, 2023: AI Risk Management Framework
A voluntary framework for considering AI risks; no Xyncwave certification is implied.
- 02OWASP, n.d.: Top 10 for LLM Applications
Threat categories to consider when connecting models to information and tools.
- 03OpenTelemetry, n.d.: Observability primer
Guidance on correlating telemetry across services.
Test the foundations before the model.
Bring one operational task and its information and permission boundaries. Assess whether the surrounding system is ready for a safe pilot.
Assess Your AI Readiness